Third-party risk, assessed from evidence and watched every day.
No chasing third parties.
No reading every page.
No guessing what matters.
ThirdPartyIQ is the intelligence layer for third-party risk. We watch the companies your organization depends on, every day, and tell you what to do when something changes. The evidence gets collected, reviewed, and checked against what you require of each third party, and what reaches your team is the impact and a recommendation, not another dashboard.
Get in touch
- of the questionnaire work eliminated
- 80% of the questionnaire work eliminated
- to collect, read, and report on a third party
- <1 day to collect, read, and report on a third party
- risk domains watched every day
- 6 risk domains watched every day
The annual review is a snapshot. Risk is continuous.
A third party’s risk does not hold still for twelve months. Between one review and the next it can lose a major customer, suffer a breach, face a lawsuit, or let a control quietly lapse, and you find out at the next questionnaire, if you find out at all. Programs stay annual not because anyone believes that is enough, but because a real assessment is built on manual work. The evidence exists. Collecting it, reading it, and making sense of it takes hours no team has.
The three jobs that keep reviews annual
01
Chasing documents
Chase the third party. Find the portal. Get access. Ask again next year.
02
Reading documents
Every page, by hand. Exceptions missed. No comparison against last year’s report.
03
Judging alerts
Feeds are a data dump. Most of it is noise. What does this one mean for us, and what do we do about it?
Do those three jobs every day instead of once a year, and the snapshot becomes a live view.
Four agents, in the order the work happens
The agents do the gathering and the reasoning. Your team makes the decision. Every recommendation arrives with the evidence behind it cited, and nothing becomes a work product without a named human approval.
01
CollectIQ
Collect, without asking
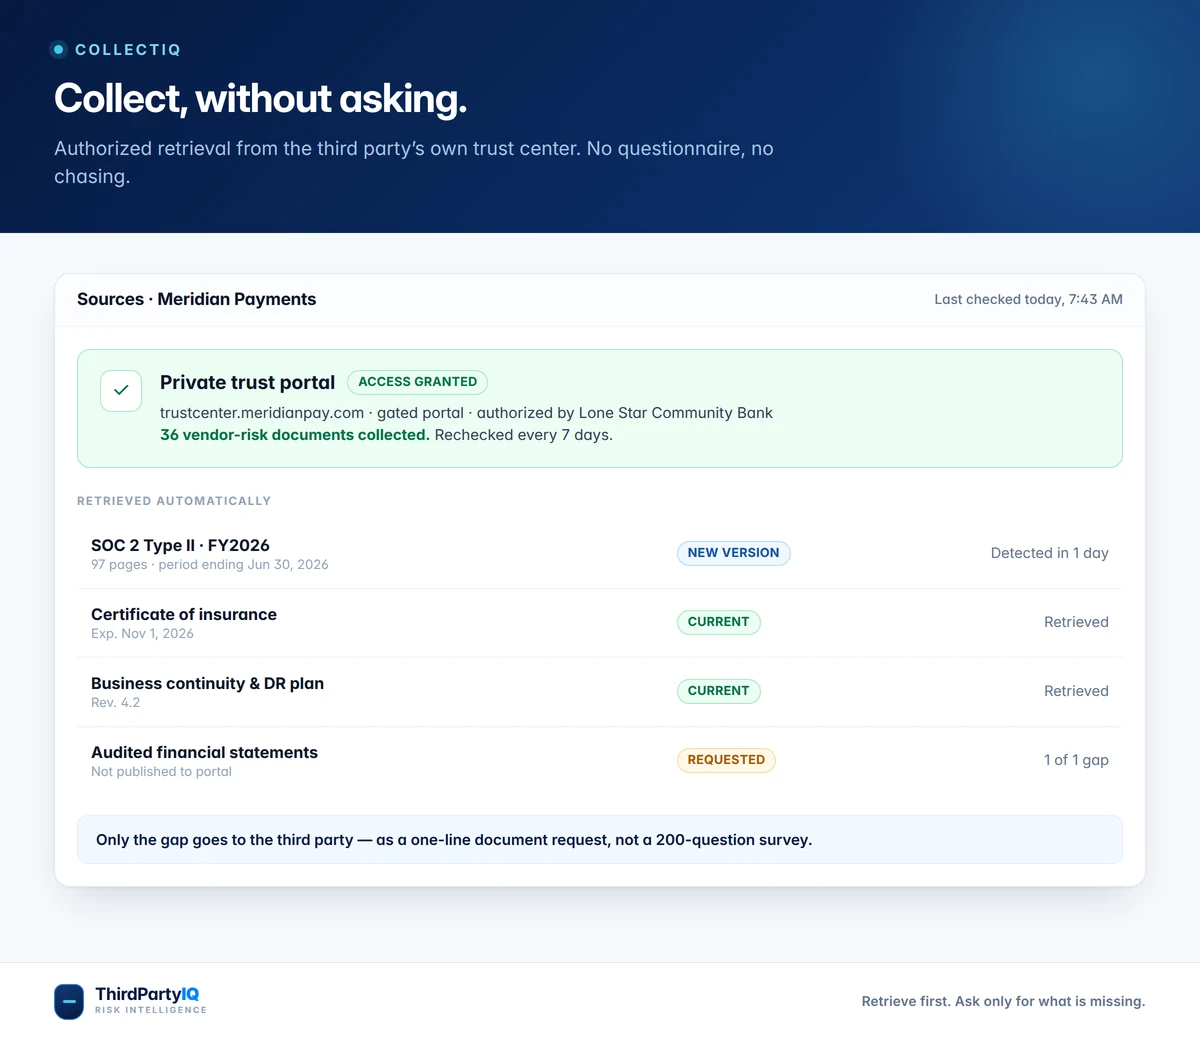
CollectIQ finds each third party’s trust center and retrieves SOC 2 reports, insurance certificates, financial statements, and continuity plans on your authority, then detects new versions the day they appear. Only what cannot be retrieved is requested, as a short document list rather than a questionnaire.
02
ReviewIQ
Every page read, every finding cited
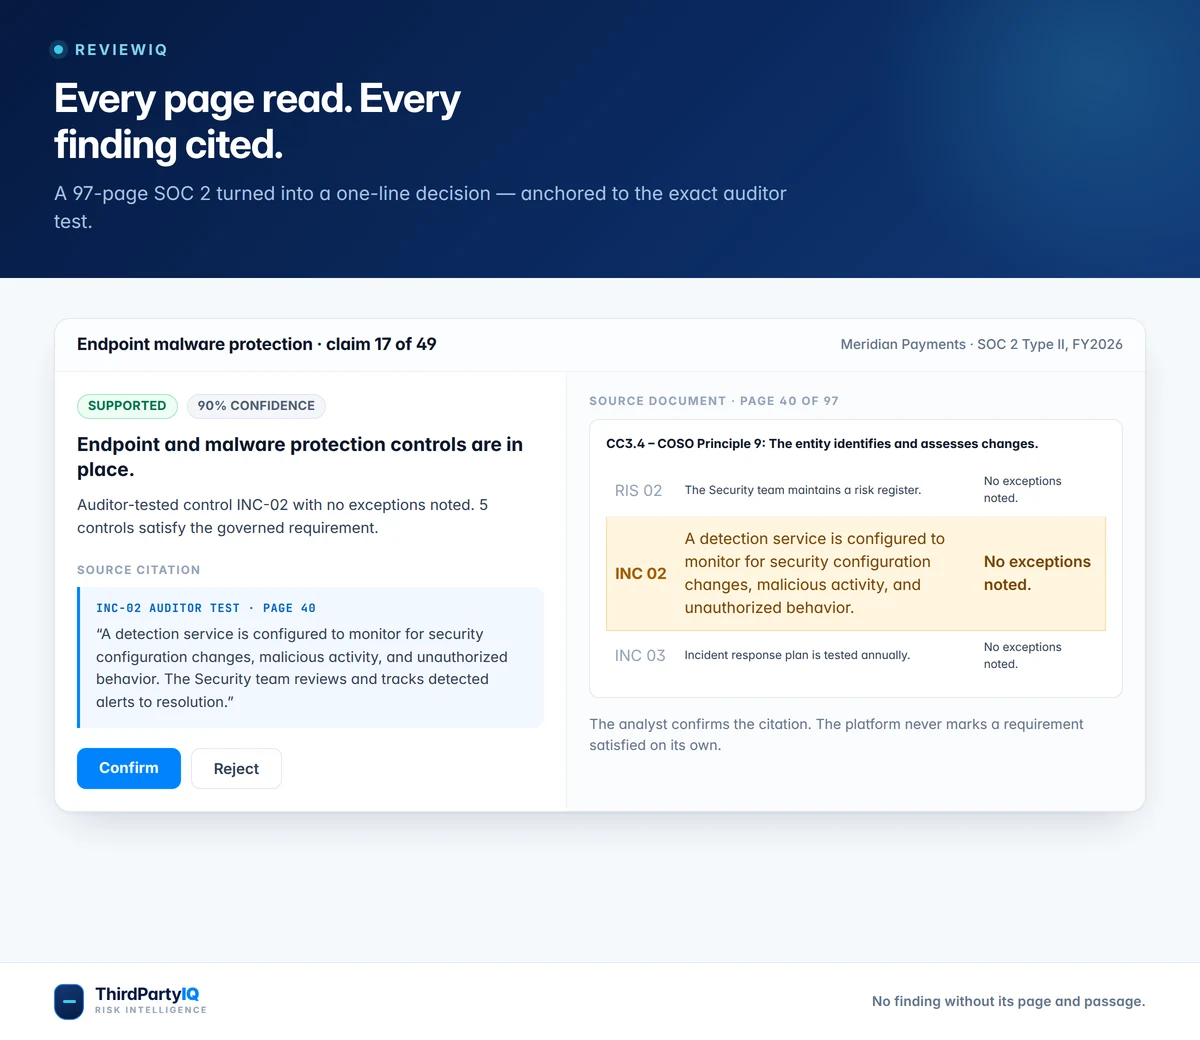
Each document is read in full and returned as a cited report: exceptions and the controls they affect, controls pushed back onto you, systems left out of scope, subprocessors and fourth parties, bridge letter gaps, and everything that changed since the last version.

03
AssessIQ
Your requirements, verified from evidence
AssessIQ starts from what you require of a third party, not from a questionnaire. Each requirement is verified directly against the collected documents and external signals, with a citation and a confidence level, before anyone contacts the third party. The evidence then maps back to your control library and to whichever assessment questionnaire you need to complete. What is left is a short residual list. Where a third party’s own answers contradict the evidence, you see it.
04
MonitorIQ
What the change means for you
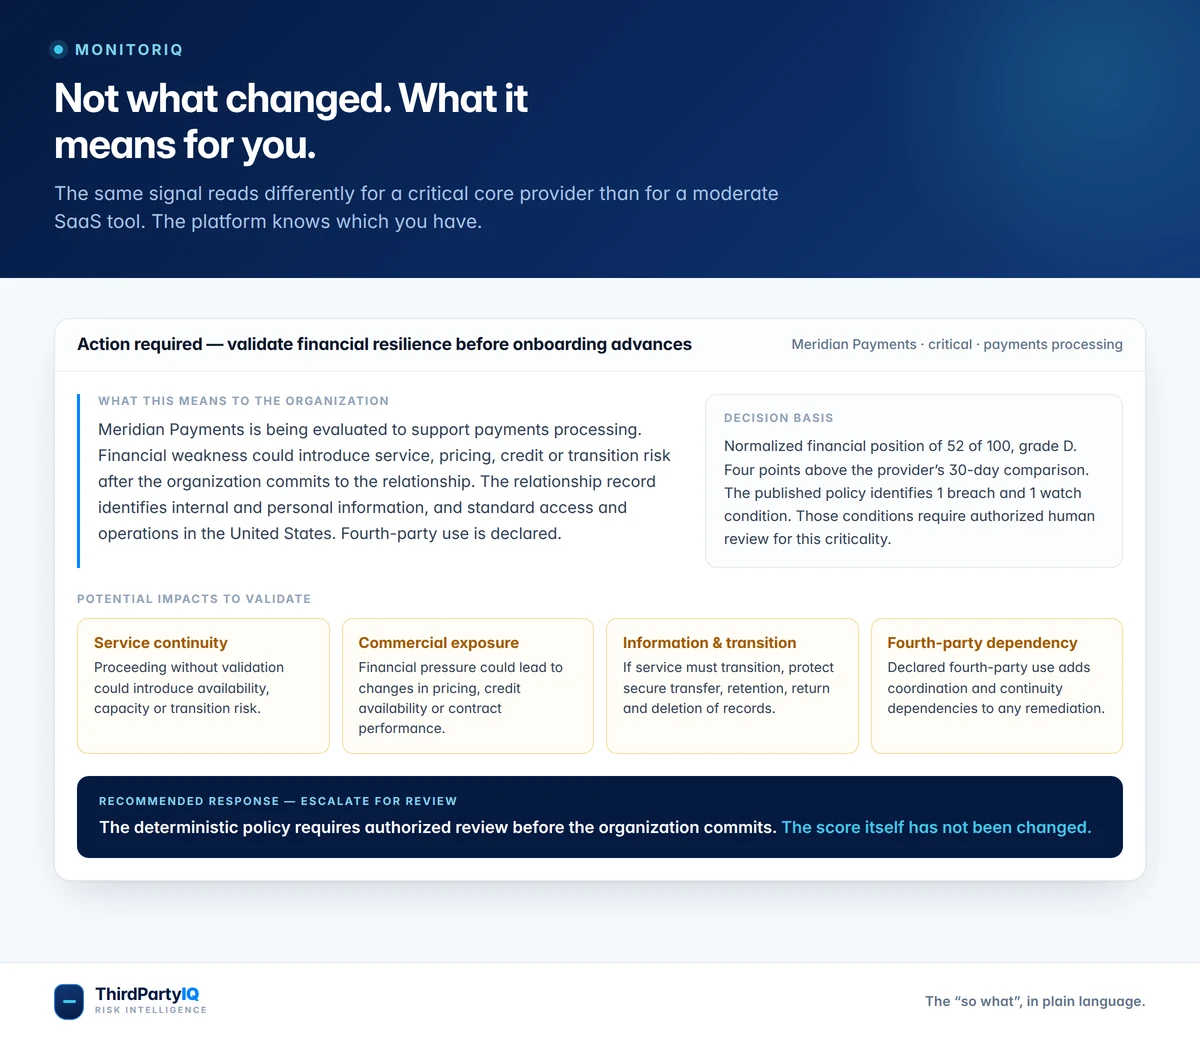
Six risk domains and every document a third party publishes, watched daily. Each change is weighed against how critical that third party is and what it actually does for you, so what reaches you is a finding with its impact stated and an action recommended, not another alert.
The same intelligence, across every business relationship
Third-party risk is where we start, and the question is the same for every external party you depend on. ThirdPartyIQ reads signals across six risk domains and assesses vendors, suppliers, borrowers, commercial customers, and counterparties from one intelligence layer.
Risk domains we read
- Financial health
- Cybersecurity
- Sanctions
- Legal
- Reputational
- Regulatory
Third-party documents we collect
- SOC 2 reports
- Bridge letters
- Security & privacy attestations
- Business continuity plans
- Disaster recovery plans
- Insurance certificates
- Financial statements
- Policy documents
Collected on your authority and kept current as new versions are published, then read in full and returned as structured, cited evidence.
Payment data we reconcile against
- Accounting
- Accounts payable
- ERP
- Procurement
Most programs assess the third parties they know about. Reconciling against what you actually pay surfaces the ones that never entered the program at all, which is usually where the unmanaged exposure has been sitting.
Relationships we assess
- Vendors & third parties
- Suppliers & supply chain
- Fintech partners
- Commercial borrowers
- Business counterparties
Financial services we serve
- Banks & credit unions
- Insurance
- Investment firms
- Wealth management & trust
- Family offices
Also serving
- Healthcare
- Life sciences
- Medical devices
- Technology & SaaS
- Manufacturing & distribution
Built differently, for a reason
We collect the evidence, not just the data
Most platforms send out questionnaires and hand you static documents and data feeds. Our agents retrieve the source documents, keep them current, and review them. That is what lets each of your requirements be verified before anyone is asked to fill out a form.
AI recommends. Humans approve.
AI does the reasoning and shows its work. Every recommendation is evidence-cited, and nothing moves forward until someone on your team approves it. Each decision is logged with who made it and the evidence behind it, and the full audit trail is exportable for an examination or an audit.
Additive by design
ThirdPartyIQ works alongside the GRC, third-party risk, and procurement systems you already have, and just as well for teams running on spreadsheets and email. Nothing to rip out.
Built to the standard of the most heavily examined industry
Financial services sets the highest bar for third-party oversight, so that is the bar we built to. Every finding carries the evidence, the reasoning, and the approval behind it.
Healthcare, life sciences, and technology companies each have their own version of the same expectation, and auditors ask for it everywhere else: documented diligence proportionate to criticality, monitoring that does not stop between reviews, and a record of who decided what and why. If you are accountable for third parties, the standard applies whether or not an examiner is the one enforcing it.
Built by a team that has done this before
ThirdPartyIQ was founded by Carl McCauley and Chris Duden, who spent nine years building governance, risk, and compliance software for financial services organizations. We know what it takes to earn a risk team’s trust.
We have spent our careers building software that risk and compliance officers, procurement teams, and supplier and vendor management teams use every day, and putting it into production inside regulated organizations.
About the companyReady to see risk before it becomes a finding?
Tell us where third-party risk management costs your team the most time today. We’ll show you how we take that work off the team.
Get in touch